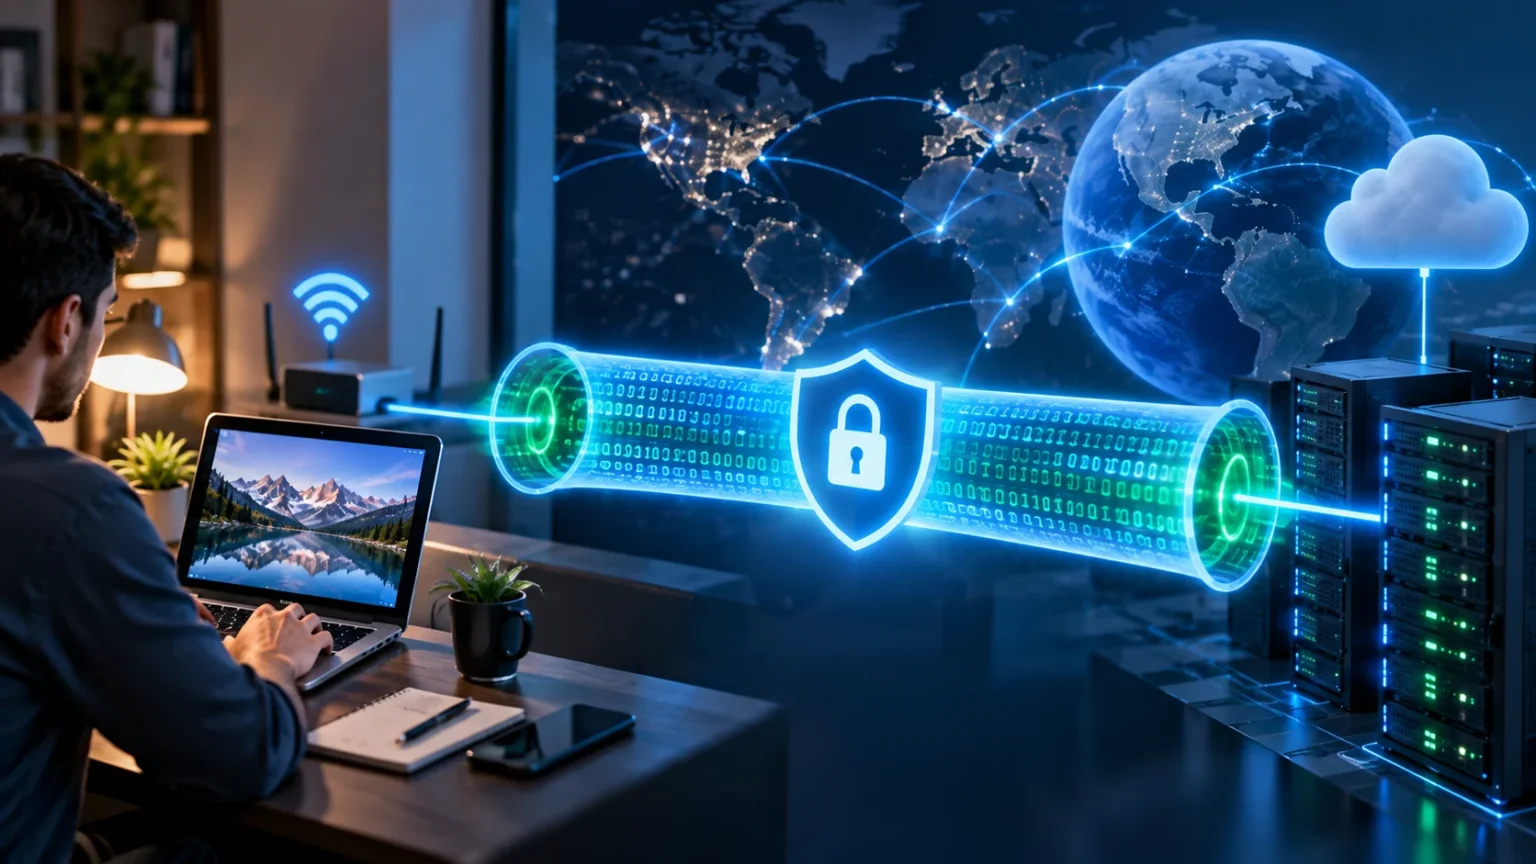

A VPN tunnel is a protected connection that allows data to travel between your device and another network endpoint over the internet. Instead of sending traffic openly through ordinary network paths, a virtual private network encapsulates and usually encrypts that traffic. This process can help protect information from being easily read while it moves across untrusted networks.
VPN tunnels are widely used by remote employees, businesses, travelers, and everyday internet users. Companies may connect distant offices through encrypted tunnels, while individuals often use VPN services on laptops or phones. Understanding how VPN tunneling works makes concepts such as encryption, VPN protocols, IP addresses, authentication, and remote network access much easier to understand.
What Is a VPN Tunnel?
A VPN tunnel is a logical connection created between two endpoints across another network, commonly the public internet. Data traveling through the tunnel is encapsulated inside additional network packets so it can move between the endpoints. Many VPN technologies also encrypt the original information to help protect its confidentiality during transmission.
The word “tunnel” is useful because the original traffic is effectively carried inside another communication layer. Your device may send normal web, application, or network traffic into the VPN software, which packages that data according to the selected protocol. The receiving VPN endpoint removes the outer layer and forwards the original traffic toward its intended destination.
A VPN tunnel is virtual rather than a dedicated physical cable between two locations. The underlying data still travels through ordinary routers, internet providers, and network infrastructure. What changes is how the traffic is packaged, protected, authenticated, and routed while moving between the two VPN endpoints.
How Does a VPN Tunnel Work?
When you activate a VPN connection, your device first communicates with a VPN server or gateway. The two endpoints establish a secure session using the settings required by the VPN protocol. Authentication may confirm the user, device, server, or combination of these before protected traffic begins moving through the tunnel.
Once the tunnel is established, selected network traffic is encapsulated and typically encrypted before leaving your device. Intermediate networks can still transport the packets because the outer addressing information remains usable for routing. However, properly encrypted contents inside the tunnel are designed to be unreadable to parties that do not possess the required cryptographic keys.
The VPN server receives the protected traffic, verifies and decrypts it, then forwards the original request toward its destination. Responses travel back to the VPN server, enter the encrypted tunnel, and return to your device. This process happens continuously while the VPN session remains active and can occur quickly enough that users barely notice it.
What Is VPN Encapsulation?
Encapsulation is the process of placing one network packet inside another packet or protocol structure. A VPN uses this technique so original traffic can travel through a network that may not directly support or trust the internal communication. The outer packet tells the internet how to move data between the VPN endpoints.
Imagine sending a letter inside another securely prepared package. The delivery system primarily sees the outer packaging and destination, while the original message remains inside. VPN encapsulation works differently at a technical level, but the comparison helps explain why the original packet can be transported through another network without being exposed in its normal form.
Encapsulation does not automatically guarantee confidentiality. Some tunneling technologies can encapsulate traffic without strong encryption, while modern VPN configurations commonly combine tunneling with cryptographic protection. When evaluating a VPN, it is therefore important to understand both the tunneling protocol and the encryption and authentication methods used alongside it.
How VPN Encryption Protects Data
Encryption converts readable data into a form that cannot easily be understood without the correct cryptographic key. When a VPN encrypts traffic, someone observing packets between your device and the VPN server should not be able to read the protected contents directly. This can be particularly valuable on networks you do not fully trust.
The exact encryption method depends on the VPN protocol and configuration. Modern VPN technologies can use strong cryptographic algorithms and secure key-exchange methods to establish protected sessions. Security still depends on correct implementation, strong authentication, current software, and appropriate configuration rather than simply displaying a “VPN connected” message.
A VPN does not encrypt every part of every internet interaction forever. Traffic is protected while traveling through the VPN tunnel, but after it leaves the VPN server, other protections such as HTTPS remain important. VPN encryption should therefore be viewed as one security layer rather than a replacement for secure websites, strong passwords, or updated devices.
What Happens to Your IP Address in a VPN Tunnel?
When you browse the internet without a VPN, websites commonly see the public IP address associated with the network sending your traffic. When you route internet traffic through a VPN server, websites generally see the VPN server’s public address instead. Your connection appears to originate from that server rather than directly from your normal internet connection.
Your actual device still needs local and network addresses to communicate with the VPN server. A VPN does not make IP addressing disappear. Instead, it changes the path traffic follows and can present the VPN endpoint’s address to internet destinations reached through the tunnel.
This behavior is one reason VPNs are commonly used for privacy and remote connectivity. However, an IP address is only one piece of information websites and services may use. Cookies, account logins, browser characteristics, and other identifiers can still associate activity with a particular user, so a VPN should not be treated as complete online anonymity.
Common Types of VPN Tunnels
Remote-access VPNs connect individual users to a VPN server or private organizational network. Employees working from home may use this arrangement to reach internal applications, file systems, or other company resources. Consumers also use remote-access VPN services when they want their internet traffic to travel through a provider’s server.
Site-to-site VPNs connect entire networks rather than individual user devices. A company may establish a tunnel between the local network at headquarters and another office in a different city. If you are learning how these locations connect, understanding LAN vs WAN concepts provides useful background for seeing how VPN tunnels can securely link separate networks across wider distances.
VPN tunnels can also differ based on how much traffic they carry. A full-tunnel configuration routes most or all relevant traffic through the VPN, while split tunneling sends only selected destinations through it. Each approach has advantages and tradeoffs involving security, performance, bandwidth, and access to local network resources.
What Is Full-Tunnel VPN Routing?
Full-tunnel VPN routing sends nearly all internet-bound traffic from the device through the VPN connection while it is active. Instead of using the normal internet gateway directly for websites and applications, traffic first travels to the VPN server. The server then forwards those requests toward their external destinations.
This setup gives organizations more centralized control because traffic can pass through corporate security systems, filtering policies, or monitoring tools before reaching the internet. Consumer VPN services also commonly use full tunneling so websites see the VPN server’s public IP address rather than the user’s normal public address.
The disadvantage is that sending everything through the VPN can increase bandwidth usage and sometimes add latency. If the VPN server is geographically distant or overloaded, performance may decline. Network administrators therefore balance security requirements with speed, server capacity, and the types of applications employees need to use.
What Is Split Tunneling?
Split tunneling allows some traffic to travel through the VPN while other traffic uses the normal internet connection directly. For example, a remote employee might send company application traffic through the corporate tunnel while streaming ordinary internet content outside it. This can reduce unnecessary load on business VPN infrastructure.
The main advantage is efficiency. Local or public internet traffic does not always need to travel through a distant corporate server and return again. Keeping selected traffic outside the tunnel can reduce latency and preserve VPN bandwidth for applications that actually require secure access to private resources.
Split tunneling also introduces security considerations because the device simultaneously interacts with protected and unprotected networks. Organizations may restrict or disable it when security policies require all traffic to pass through centralized controls. Whether split tunneling is appropriate depends on device management, risk tolerance, application needs, and network architecture.
Popular VPN Tunneling Protocols
WireGuard is a modern VPN protocol known for a relatively small codebase and efficient performance. It uses contemporary cryptographic techniques and is supported by many operating systems, routers, and VPN services. Its streamlined design can make configuration and performance attractive for both consumer and professional use cases.
OpenVPN is another widely used VPN technology and has been deployed for many years. It can operate using different transport methods and offers extensive configuration options. This flexibility has made it popular for business and consumer VPN applications, although actual performance depends heavily on settings, hardware, and network conditions.
IPsec is frequently used for site-to-site and enterprise VPN connections and can protect IP traffic using established security mechanisms. IKE is commonly involved in negotiating secure IPsec sessions. Other tunneling technologies exist as well, but protocol selection should consider security, compatibility, performance, management requirements, and current software support.
VPN Tunnels for Remote Work
Remote workers often need secure access to resources that are not exposed directly to the public internet. A VPN tunnel can connect an employee’s device to the organization’s network and make selected internal services reachable. Depending on the setup, the remote device may behave as though it has a protected path into the company environment.
Authentication is especially important for remote-access VPNs because organizations need confidence that only authorized people and devices can connect. Passwords may be combined with certificates, multifactor authentication, device checks, or identity platforms. Strong authentication reduces the risk that stolen credentials alone will provide access to internal resources.
Businesses should also keep VPN software, gateways, and connected devices updated. A secure tunnel cannot protect an organization if an attacker compromises the VPN server or an authorized endpoint through another vulnerability. Remote access should therefore be part of a broader security strategy that includes updates, access control, monitoring, and least-privilege permissions.
Does a VPN Tunnel Make You Completely Private?
A VPN can prevent your local internet provider or nearby network observers from easily seeing the contents of properly encrypted traffic inside the tunnel. They can generally still determine that your device is communicating with a VPN endpoint. The VPN provider, meanwhile, occupies a trusted position because traffic passes through its infrastructure.
Websites may still identify you through accounts, cookies, browser storage, fingerprinting, and other technologies. Logging into the same social media or email account, for example, reveals your account identity regardless of whether the connection comes through a VPN. Changing an IP address therefore does not automatically create complete anonymity.
VPN providers also differ in their privacy practices, technical designs, jurisdictions, and logging policies. Users should evaluate providers carefully rather than assuming every service offers identical protections. A VPN is best understood as a tool for securing and routing network traffic, not as a universal solution for every privacy or security concern.
Can a VPN Tunnel Slow Down Your Internet?
A VPN can add some overhead because traffic must be encrypted, encapsulated, routed through the VPN server, decrypted, and then forwarded toward its destination. The additional network path may increase latency, particularly when the server is far away. Encryption also requires processing resources on the device and VPN server.
The impact may be small on a well-designed service with nearby servers and modern hardware. Other situations can produce more noticeable slowdowns, especially when servers are congested or the underlying internet connection already has high latency. Different VPN protocols and configurations can also perform differently on the same connection.
Choosing a server closer to your physical location often reduces unnecessary distance. Updating the VPN application and testing alternative supported protocols may also improve performance. However, a VPN cannot make every network problem disappear, so slow speeds can still result from Wi-Fi interference, provider congestion, server limitations, or the destination website itself.
VPN Tunnel Security Best Practices
Use modern VPN protocols and current software rather than relying on outdated technologies simply because they remain available. Security standards evolve, and older protocols may contain weaknesses or use cryptographic methods that are no longer recommended. Businesses should periodically review VPN infrastructure instead of assuming a configuration remains secure forever.
Enable strong authentication wherever possible. Multifactor authentication can provide an additional layer of protection if a password becomes compromised. Organizations should also restrict VPN users to the systems they actually need rather than allowing every remote account unrestricted access to the entire internal network.
Monitor VPN activity for unusual logins, repeated authentication failures, unexpected geographic patterns, and abnormal traffic. Keep gateways patched and remove unused accounts promptly. Combining secure tunneling with endpoint security, access controls, logging, encryption, and user education provides stronger protection than depending on the VPN tunnel alone.
Conclusion
A VPN tunnel creates a protected logical connection across another network, usually the public internet. It works by encapsulating traffic and, in modern VPN setups, encrypting that information between the connected endpoints. The VPN server or gateway then decrypts and forwards the original traffic toward its destination.
Different VPN configurations solve different problems. Remote-access VPNs connect individual users, site-to-site tunnels link separate networks, full tunneling routes most traffic through the VPN, and split tunneling protects only selected traffic. Protocols such as WireGuard, OpenVPN, and IPsec provide different approaches to establishing these protected connections.
VPN tunnels can improve privacy and secure remote communication, but they are not a complete security solution by themselves. Strong authentication, updated software, HTTPS, endpoint security, careful provider selection, and sensible access controls still matter. Understanding these limitations helps you use VPN technology for what it does best: protecting and routing network traffic between trusted endpoints.
FAQs
What is a VPN tunnel in simple terms?
A VPN tunnel is a protected connection that carries network traffic between two endpoints over another network. It usually combines encapsulation and encryption to make the transmitted data harder for unauthorized parties to read.
Does a VPN tunnel hide my IP address?
For internet traffic routed through the VPN, websites generally see the VPN server’s public IP address rather than your normal public address. This does not make you completely anonymous online.
What is the difference between a VPN and a VPN tunnel?
A VPN is the broader private networking system, while the tunnel is the logical protected path used to carry traffic between VPN endpoints. A VPN may create one or more tunnels.
Is split tunneling safe?
Split tunneling can be useful and efficient, but it allows some traffic to bypass the VPN. Whether it is appropriate depends on security policies, device protection, application requirements, and the risks involved.
Can a VPN tunnel be hacked?
No technology is completely immune to attack. Strong modern protocols, updated VPN software, secure authentication, patched servers, and proper configuration significantly reduce risk compared with outdated or poorly managed VPN deployments.